Source code stories
Financial institutions still face hidden fourth-party risks even after Microsoft, Google Cloud, AWS and Oracle were designated as critical providers.
Attackers turned a newly disclosed Gitea flaw into automated intrusions within days, hitting systems in five countries and exposing source code and secrets.
Many firms still cannot stop AI agents from causing damage before execution, leaving systems exposed to production outages and data loss.
Attackers are exploiting AI faster than many defences can respond, prompting a shift to continuous testing for hidden exposures.
Attackers are exploiting AI tools to speed intrusions and drain cloud resources, pushing defenders towards machine-speed security operations.
Autonomous systems are now creating fresh avenues for code theft, remote execution and runaway cloud spending, Mandiant says.
The private previews aim to help security teams spot exploitable code chains and connect AI agents to Rubrik's governance tools more safely.
Security-conscious banks and defence agencies can now keep Cursor agents on their own infrastructure, reducing exposure of code, secrets and audit data.
Independent testing found no critical, high or medium flaws in TiDB's platform as database buyers demand stronger proof of security.
The deal extends Fortinet's reach into AI runtime protection as companies race to secure agents, models and tools across production systems.
Developers can now scan C code earlier in the process, as Endor Labs says its buildless AI SAST found 96 of 102 known bugs in tests.
In two days, the system uncovered more than 100 critical bugs in stolen code repositories, outpacing manual review and aiding incident response.
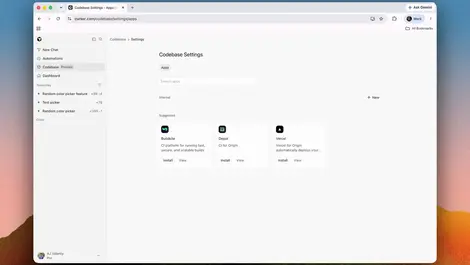
Paid Cursor subscribers can now host repositories and manage pull requests in one place, as Origin enters early beta against GitHub and GitLab.
The new tool aims to speed enterprise app building while keeping AI-generated outputs governable, auditable and easier to deploy safely.
Prompt-injection attacks and data leaks are the main risks as businesses connect Copilot and Gemini to email, files and internal tools.
The tie-up aims to help security teams turn validated AI findings into ranked fixes before vulnerabilities pile up and attackers move first.
Boards are under pressure to curb staff use of ChatGPT and similar tools, as pasted data could expose customer records and source code.
Organisations using Wayfinder Frontier AI Services will now get help turning validated vulnerabilities into prioritised fixes and post-deployment checks.
Local hosting in Sydney eases compliance worries for Australian firms using AI tools that may expose prompts, code and credentials.
Software teams using AI coding agents face faster pull request volumes, as Harness pairs a new repository with risk-based review tools.